- Which authentication sources does ProVide support?
- Does ProVide support multiple domains and AD trust relationships?
- Can I control settings for AD users and security groups in ProVide?
- What happens when a Windows user logs in to ProVide?
- What is Windows account impersonation in ProVide?
- Which Active Directory tokens can I use in ProVide?
- Where do I configure Active Directory authentication in ProVide?
How does ProVide authenticate Windows and Active Directory users?
ProVide handles Windows and Active Directory (AD) authentication automatically, with no need to manually import users or sync user data. You can also apply ProVide settings, such as login limits, bandwidth management, and home directory contents, to individual Windows users or entire Windows security groups connecting over FTP and SFTP.
Which authentication sources does ProVide support? #
ProVide supports authentication using:
- An Active Directory domain
- A Windows Server, either local or remote
Does ProVide support multiple domains and AD trust relationships? #
Yes. You can specify several domains separated by a pipe character (|) to support Active Directory trust relationships.
Can I control settings for AD users and security groups in ProVide? #
Yes. You can link a ProVide account to a Windows account, or a ProVide group to a Windows security group.
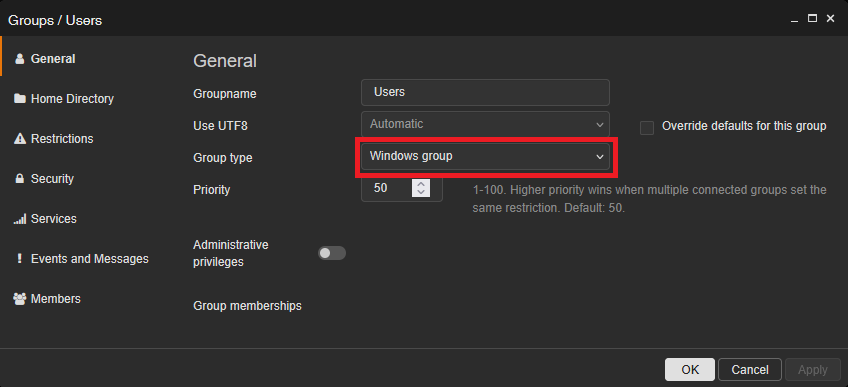
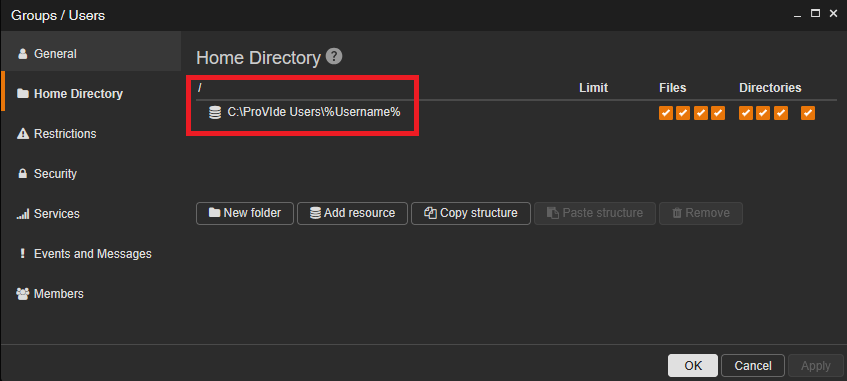
A linked user gets the account settings you define in ProVide, including login limits, bandwidth management, and specific home directory contents. A linked group applies default settings to every user in that Windows group, helping you manage thousands of accounts.
For example, use the %USERNAME% token in a resource path so each user automatically gets their own folder.
What happens when a Windows user logs in to ProVide? #
ProVide’s own accounts and settings always take precedence. At login, ProVide checks whether the user:
- Exists as a regular ProVide account
- Exists as a ProVide account linked to Windows
- Passes Windows authentication
After gathering the relevant user data, ProVide completes a normal server login. Restrictions and security settings configured in ProVide on accounts and groups linked to Windows are enforced when those users log in.
What is Windows account impersonation in ProVide? #
With impersonation, each connection runs as the corresponding Windows user, so Windows access rights and security restrictions apply automatically.
If a folder is readable only by a specific Windows user, that user can read it through ProVide after authenticating. Impersonation also applies to network (UNC) paths, allowing Windows permissions to govern access to those resources.
Which Active Directory tokens can I use in ProVide? #
ProVide supports the following Active Directory tokens for configuring resources for Windows users:
%AD_DISPLAYNAME%%AD_HOMEDIR%%AD_COMMENT%%AD_SCRIPT%%AD_PHONE%%AD_MAIL%
For example, link a ProVide group to the Windows security group “Domain Users” and use %AD_HOMEDIR% as its home directory resource path. Each user in that linked group automatically gets their own home directory.
Where do I configure Active Directory authentication in ProVide? #
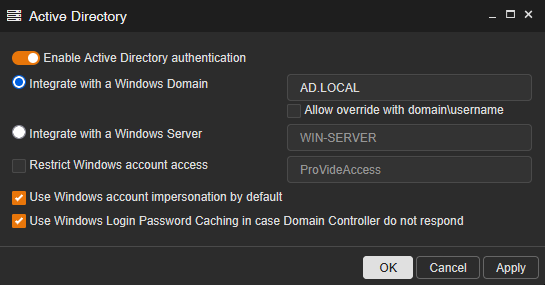
To open the Active Directory settings in ProVide:
- Log in to the ProVide web admin interface with an account that has admin privileges.
- Click the Access tab in the upper left corner.
- Click Active Directory in the top menu.
In the Active Directory settings window, you can enable Active Directory authentication and choose whether to integrate with a Windows domain or a Windows Server.